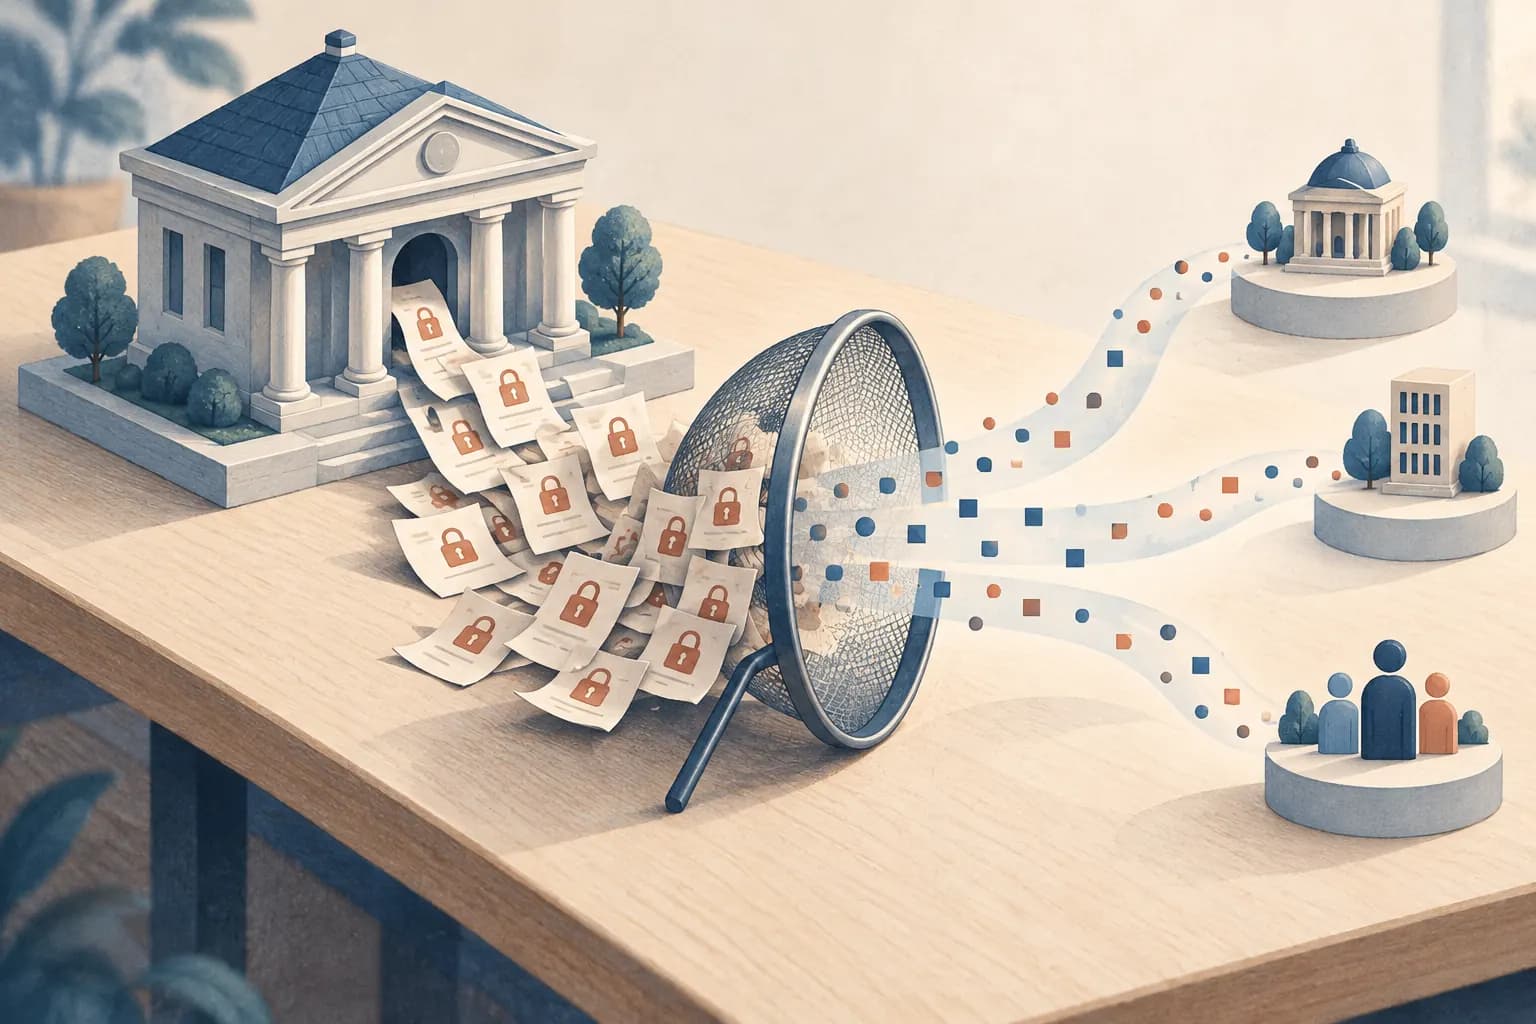
Banks and credit unions can measure which campaigns lead to funded accounts without placing account data in ad platforms or analytics tools. Keep account numbers, balances, loan details, and application content in systems built to hold them, and send outside only the signals your counsel has approved. Review the payload and destination, not just the event name.
What does GLBA say about sharing customer information?
The Gramm-Leach-Bliley Act requires financial institutions to protect and limit the sharing of consumers’ nonpublic personal information. Its privacy provisions are implemented by Regulation P, the CFPB’s Privacy Rule at 12 CFR Part 1016. The CFPB’s summary says covered institutions include banks, savings associations, and credit unions, as well as non-bank lenders and other financial companies.
The same summary says the regulation requires certain privacy notices, limits disclosure of nonpublic personal information to nonaffiliated third parties, and gives consumers the right to opt out of certain disclosures. Exceptions decide which flows need an opt-out, so read the notice and opt-out sections with counsel. The rule does not mention pixels or tags. Whether a given tag is a disclosure it covers is a question about your own data flow.
Safeguards rules are split by regulator as well. The FTC Safeguards Rule applies to financial institutions subject to the FTC’s jurisdiction. Banks and credit unions answer to their own regulators, so ask counsel which safeguards framework applies to your charter and to any non-bank partner, such as a fintech or lending platform, that touches the application flow.
What should never reach an ad platform or analytics tool?
Google’s PII policy is a useful floor. Google asks that no data be passed that it could use or recognize as personally identifiable information, and it warns that visitors sometimes type PII into form fields and search boxes. A financial institution has more reasons to be careful than that floor implies, because account and loan details can identify a person even without a name attached.
| Data element | OK in ad or analytics platforms? | Safer alternative |
|---|---|---|
| Account, loan, or card number in a URL, title, or event | No | Use an internal record ID that has no meaning outside your systems, and keep it out of URLs. |
| Balances, transactions, or credit score | No | Keep them in the core banking or servicing system. |
| Loan amount, product type, or application stage tied to a person | No | Report a generic “application started” or “application submitted” event with no product or amount. |
| Social Security number, date of birth, income, or employer captured by a form-field tag | No | Do not capture these fields in tag variables, and confirm that form-field listeners ignore them. |
| Online banking or authenticated application URLs and page titles | No, treat as a separate surface | Keep third-party ad pixels off authenticated pages, and use only tools your compliance team has reviewed. |
| Generic product category page, such as a “mortgage” or “auto loan” overview | Review with counsel | Use general category pages, with no per-person context added to the URL or event. |
| Ad click ID or UTM values, such as gclid or utm_campaign | Review with counsel before they leave the application flow | Store them on the application record at submit, and send them only where counsel approves. |
| Hashed email or phone sent for audience matching | Requires counsel review before any use | Send a generic conversion event with no contact data unless counsel approves matching. |
Why do marketing sites and online banking need different rules?
A public marketing page usually shows general information about products, rates, and branches. An online banking page or an application that has started shows the visitor’s own relationship with the institution. The same tag can be low-risk on one and inappropriate on the other, so inventory each surface separately.
Authenticated areas deserve the strictest review. Ask counsel whether any third-party tag on a logged-in page can receive account context, including page titles that name a product, and whether a vendor agreement is needed for the data it receives. Application flows are a middle case. They often start on a marketing page and then move to a form, so check every step, not only the landing page.
How do you manage vendors that receive data?
Banks have interagency guidance on third-party relationships. The 2023 interagency guidance from the OCC, the Federal Reserve, and the FDIC sets out risk management expectations for third-party relationships. The bulletin states that it applies to all banks with third-party relationships. Credit unions are overseen by the NCUA, so ask your compliance team which NCUA expectations apply to your vendors.
At a high level, a marketing vendor that receives customer-linked data belongs in the same review as any other third party: what data it receives, how it may use that data, how the contract limits reuse, and how you would detect and stop a misconfigured tag. State privacy laws add another layer, and their treatment of financial institutions and GLBA-covered data varies. Ask counsel how state privacy laws apply to your institution.
How do you measure campaigns to funded accounts?
The business still needs to know which campaigns fund accounts. The pattern that holds up is to split the work. The core system and application platform keep account and identity context under their own controls. Your warehouse holds campaign and outcome counts keyed to internal IDs. Ad platforms receive the minimum signal your counsel has approved, if any.
- Capture UTMs and click IDs when the application starts, before any redirect that could drop them.
- Write them onto the application record at submit, next to the internal record ID, rather than into a URL.
- Keep product details, amounts, and identity data in the core system, under its access controls.
- Join campaign to application, approval, and funded outcomes in your warehouse using the internal record ID.
- Decide with counsel which events, if any, go back to ad platforms, and send only generic ones.
If you filter fields before they leave your site, a server-side layer can remove or generalize values before forwarding them. The server-side tagging guide covers the implementation. A filter helps only when its rules are written down, tested, and reviewed with the people who own the data flow.
For the offline side, the offline conversions guide explains how funded-account outcomes can return to a campaign report without putting customer details into a page. The healthcare version of this problem follows a similar design, with the same split between intake records and aggregate reporting.
Before a release, run the tracking QA checklist before launch and add checks for application URLs, page titles, form fields, and authenticated pages. If a server-side container sits in the path, the server-side tracking mistakes post shows how to trace one event through it and check what each destination receives.
For an example of attribution work that connects campaigns to funded accounts, see the HIFI Agency case study. It describes an attribution engagement, not a compliance review. If you want help inventorying public pages, forms, and tags before counsel reviews them, contact us about a tracking audit. The audit does not replace a legal or compliance review.
Frequently asked questions
Does the Gramm-Leach-Bliley Act stop a bank or credit union from using ad pixels?
The GLBA does not name pixels or tags. Its Privacy Rule limits when a financial institution can share nonpublic personal information with nonaffiliated third parties, and it requires privacy notices and, in some cases, opt-out rights. Whether a particular tag triggers those limits depends on what it sends, to whom, and how the recipient may use it. Ask your counsel to review each data flow.
Is it safe to put Google Analytics on a credit union website?
Google’s guidance says not to pass any data that Google could use or recognize as personally identifiable information. Its examples include names, Social Security numbers, and email addresses, and it warns that form fields and search boxes can capture PII. Google’s page does not list account numbers, so treat them as off-limits by default. Whether your setup is appropriate is a question for your compliance team and counsel.
Does a cookie consent banner settle the question?
No. A consent banner records a visitor’s choice about cookies, but it does not decide whether the data a tag sends falls under GLBA limits or state privacy law. Document what each choice enables, verify that tags follow it, and have counsel review the data that leaves the page.
How do you measure ad campaigns to funded accounts without sending account data?
Capture campaign parameters and ad click IDs when the application starts, store them on the application record in your own systems, and join them to funded-account outcomes in your warehouse using an internal record ID. Send ad platforms only the generic conversion signals that counsel has approved, with no product, balance, or customer identifier attached.